
GitHub’s new package firewall can stop coding agents installing risky dependencies
GitHub has introduced a package firewall that can block dependency installations before a coding agent or automated build downloads them. The public preview is available to Enterprise Cloud customers, including those using data residency.
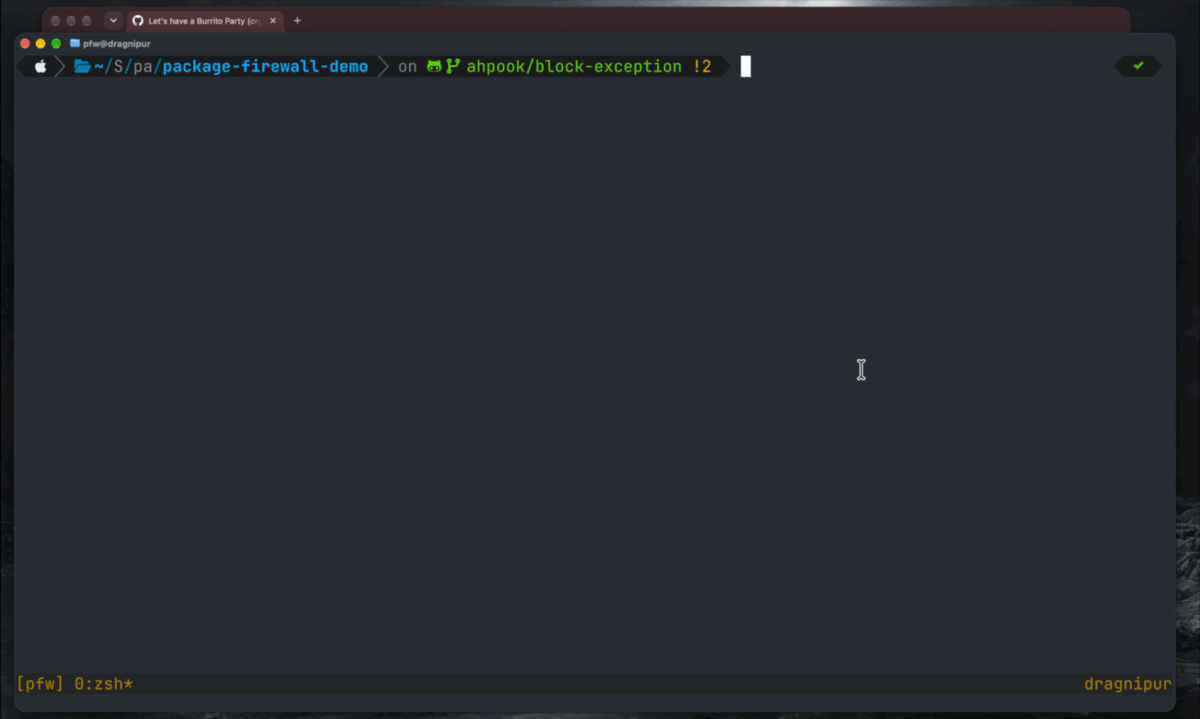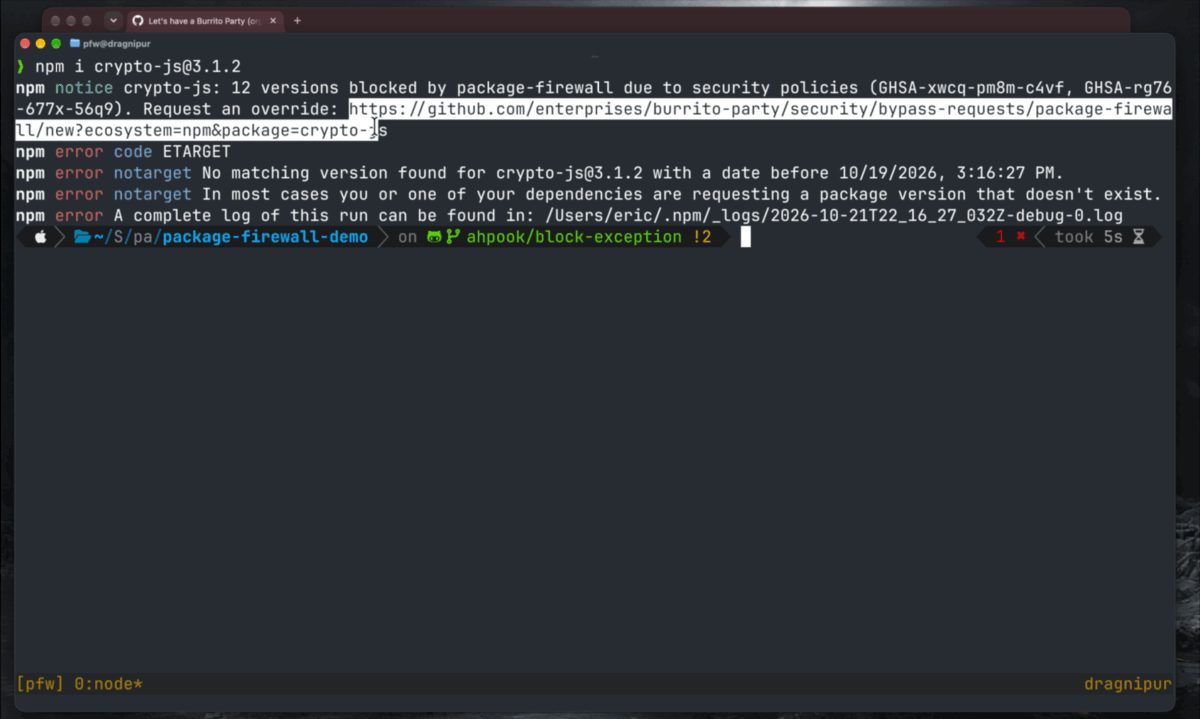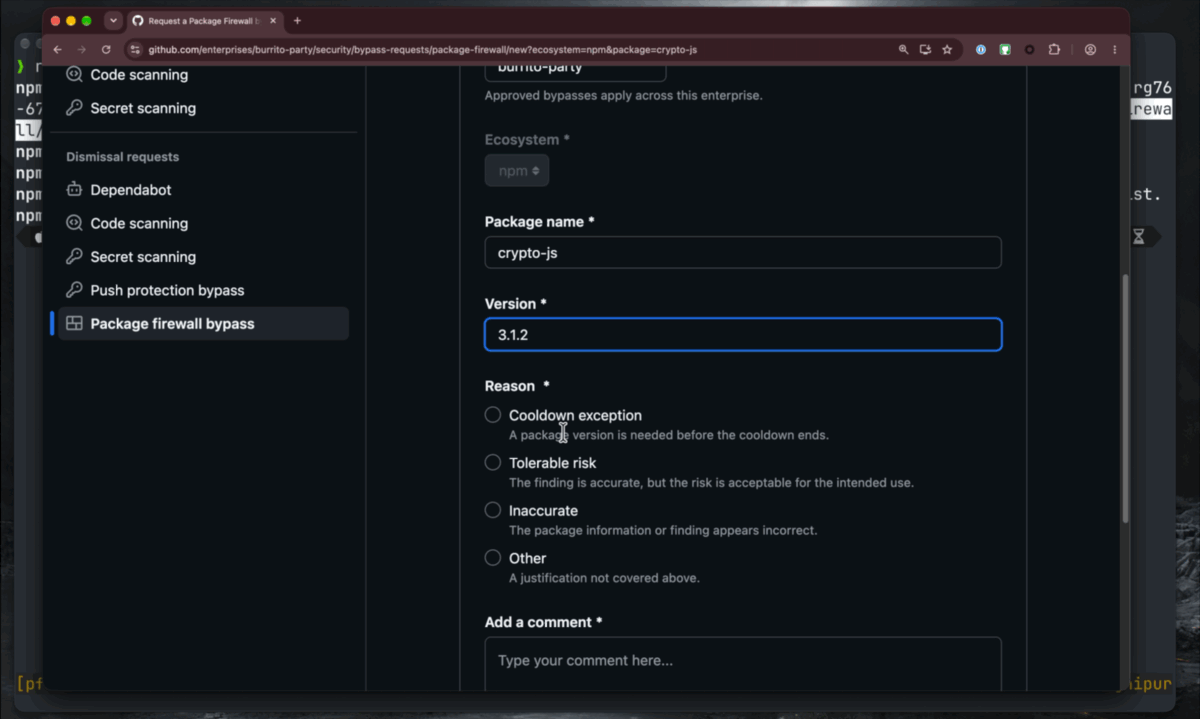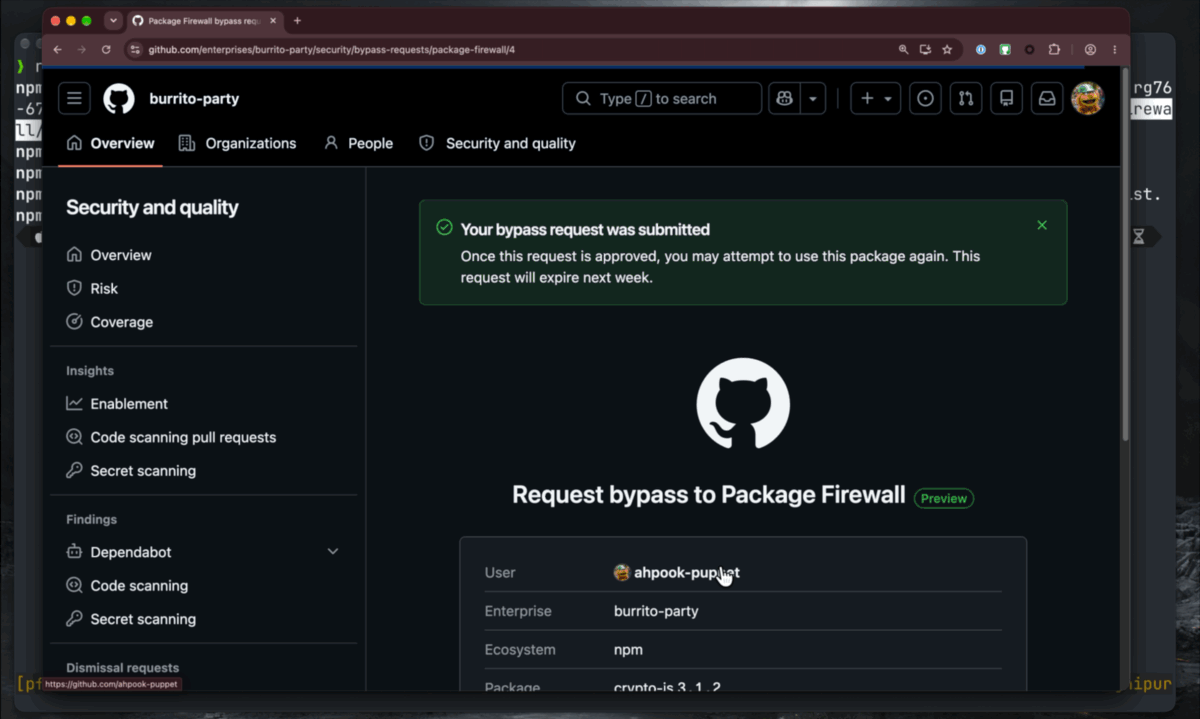
GitHub’s demonstration shows a cooldown block and the exception-request workflow. Image: GitHub
The service currently supports npm packages only. It is free during the preview, with usage-based billing planned when it becomes generally available.
The firewall checks package requests before they reach the installer
Administrators define policies, then configure endpoints or internal registries to send requests through the firewall instead of directly to upstream package repositories. Both package-list requests and the downloads themselves are evaluated.
Available controls include a cooldown period for newly published packages, checks against malware and vulnerability advisories in the GitHub Advisory Database, and supply-chain checks such as attestation downgrades.
The cooldown is intended to provide a waiting period before fresh releases can be installed. It is a policy choice, not proof that an older package is harmless or that every newly published package is dangerous.
If a package is incorrectly blocked, users can request an exception. The workflow gives administrators a way to review a specific case without abandoning the broader policy.

The GitHub Advisory Database supplies malware and vulnerability information used by the firewall. Image: GitHub
Coding agents create a reason to move checks earlier
GitHub highlights agents and CI runners because they often install dependencies while completing a task without a person reviewing each installation. An install-time gate can apply the organisation's rules at that point in the workflow.
The firewall must be configured and requests must actually pass through it. It is not described as a protection that automatically covers every development machine, package ecosystem or agent as soon as an enterprise has GitHub access.
MIXED has covered the spread of official agent integrations for development tools. As those agents take on more setup work, dependency controls become part of managing their execution environment. GitHub's initial offering is a specific npm policy gate, with broader functionality still developing during preview.

